Read this first. We are not a CPA firm, so we provide SOC 2 readiness, gap analysis and preparation consulting only. The formal SOC 2 examination and report are performed by a separate, licensed, independent CPA firm.
Guides
SOC 2 readiness guides
These SOC 2 readiness guides cover the work that happens before a CPA firm examines you. So each guide explains one control area or decision in plain words.
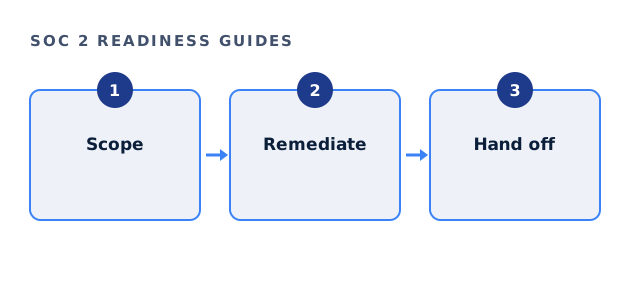
How to use these SOC 2 readiness guides
Start with cost and scope. They shape everything else. Then read the control guides for your weakest areas. Finally, plan the timeline with the implementation guide.
We are not a CPA firm. So these guides cover readiness, while the examination itself is always performed by a licensed, independent CPA firm.
Start here
Cost, scope and the first assessment. Read these first.
SOC 2 readiness guides by control area
Each control area in plain words. Also the evidence auditors sample.
- SOC 2 controls list
- SOC 2 policies
- SOC 2 risk assessment
- SOC 2 access control
- SOC 2 change management
- SOC 2 logging requirements
- SOC 2 encryption requirements
- SOC 2 backup requirements
- SOC 2 physical security requirements
- SOC 2 vendor management
- SOC 2 asset management
- SOC 2 password requirements
- SOC 2 Kubernetes
SOC 2 readiness guides on tools
Platforms that help. But they do not replace the work.
Ready to scope your readiness work?
Answer four questions and receive a written scope and price range, usually the same working day.
See if we can help