Service
SOC 2 access control that survives an access review sample
SOC 2 access control is where most first audits find exceptions. So the controls must be simple enough to run every time, and leave evidence every time.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
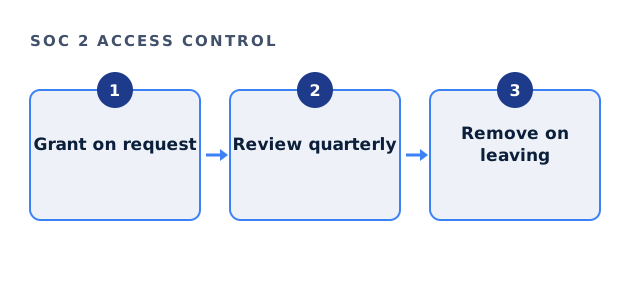
What CC6 asks for in SOC 2 access control
The logical and physical access criteria, CC6, ask that only authorised people reach systems and data. Therefore auditors test how access is granted, reviewed and removed. The criteria are in the AICPA Trust Services Criteria.
The core SOC 2 access control set
Most companies need the same core controls. However, each must fit your tools.
- Unique accounts, so no shared logins
- Multi-factor authentication on key systems
- Access granted by request and approval
- Quarterly access reviews with records
- Access removed on the day someone leaves
SOC 2 access control quick test
Tick what you could prove for a random sample.
Your result appears here as you tick, so you can see what is still open.
Evidence auditors sample
Auditors pick samples, such as five joiners and five leavers. So every event needs a record.
| Control | Evidence sampled |
|---|---|
| Onboarding | Approved request before access was granted. |
| Offboarding | Removal time compared with the leaving date. |
| Access review | Signed review with changes made. |
| MFA | Settings screenshots for each key system. |
Where SOC 2 access control usually fails
Offboarding is the classic failure, because one forgotten tool keeps an account alive. Also, access reviews often happen once and never again. We fix both with simple checklists and calendar ownership.
Part of the readiness engagement
Access control work sits inside our fixed readiness fee of $5,000 to $40,000. We work alongside your engineers, while a separate licensed CPA firm examines the result.
Single sign-on deserves a mention here. Because one switch removes access everywhere, it turns offboarding from a checklist of ten tools into one action. So if you are choosing tools now, prefer ones that support it. Also keep a list of any tool outside single sign-on, since those are the accounts most often forgotten.
SOC 2 access control questions
How often should SOC 2 access control reviews happen?
Quarterly is common, although some scopes justify a different interval in policy.
Do we need single sign-on?
Not strictly, but it makes offboarding far easier to prove.
What counts as evidence for SOC 2 access control?
Tickets, approvals, review records and settings screenshots.
Does physical access matter?
Yes, under CC6, although cloud providers cover their own data centres.
Related guides
Fix SOC 2 access control before the auditor samples it
Tell us your main systems and headcount. We reply with a written scope and a fixed fee.
See if we can help