Guide
SOC 2 physical security requirements when you run in the cloud
SOC 2 physical security requirements sound like locks and badges. For a cloud-first company, however, most of that sits with the provider, so the question is what remains yours.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
What CC6.4 covers
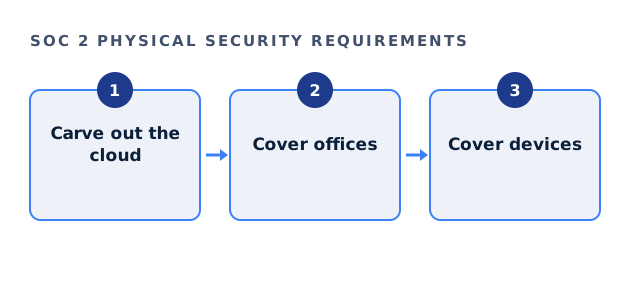
Criterion CC6.4 asks that physical access to facilities and assets is restricted to authorised people. So it applies to data centres, offices and devices that hold data. The text is in the AICPA Trust Services Criteria.
How cloud carve-outs work
Your cloud provider has its own SOC 2 report covering its data centres. Therefore your report usually carves those controls out and relies on the provider's report instead. You then read that report, which is a vendor management task.
SOC 2 physical security requirements check
Tick what applies to you.
Your result appears here as you tick, so you can see what is still open.
SOC 2 physical security requirements that remain yours
Even without a server room, some physical controls stay with you.
| Area | Typical control |
|---|---|
| Office | Visitor log and restricted access, if you have one. |
| Laptops | Disk encryption and screen lock, enforced centrally. |
| Lost devices | Remote lock or wipe, plus a reporting process. |
| Remote staff | Policy on working securely at home. |
SOC 2 physical security requirements for remote companies
With no office, SOC 2 physical security requirements shrink to devices and the provider carve-out. That is common and acceptable, as long as the scope says so clearly.
Part of readiness
We define the carve-outs and device controls inside the fixed readiness fee. The CPA firm then examines the result, because we are not a CPA firm.
Document the decision clearly. For example, a short statement that the company has no offices, uses managed laptops and relies on its cloud provider's report already answers most auditor questions. Also keep the device management report handy, because auditors often ask to see encryption status for a sample of laptops. As a result, physical security becomes one of the simplest areas of the whole engagement.
SOC 2 physical security requirements questions
Do SOC 2 physical security requirements apply to remote companies?
Partly. Devices and the provider carve-out still apply.
What is a carve-out?
Excluding a vendor's controls from your report while relying on its own report.
Do we need badge access?
Only if you have an office in scope.
Are laptops part of SOC 2 physical security requirements?
In practice, yes, because they hold data.
Related guides
Scope physical controls correctly
Tell us whether you have offices and how devices are managed. We reply with a written scope and a fixed fee.
See if we can help