Guide
The SOC 2 internal audit, before the CPA firm arrives
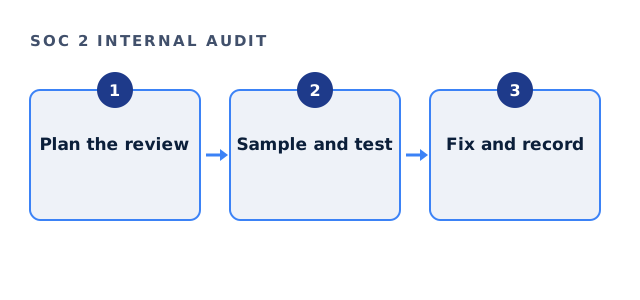
A SOC 2 internal audit tests your controls the way the CPA firm will, but earlier. So exceptions surface while there is still time to fix them quietly.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
What a SOC 2 internal audit is
It is an internal review of controls against your own SOC 2 control set. However, it is not the examination, and it produces no report for customers.
The criteria also expect monitoring activities. Therefore a periodic internal review supports the controls as well as preparing for fieldwork.
Who runs a SOC 2 internal audit
Independence matters. So the reviewer should not test controls they operate themselves.
| Option | Note |
|---|---|
| Internal audit or risk team | Independent, if one exists |
| A peer from another team | Workable for small companies |
| Outside readiness consultant | Knows what CPA firms sample |
SOC 2 internal audit readiness check
Tick what you have done this year.
Your result appears here as you tick, so you can see what is still open.
What a SOC 2 internal audit should test
Mirror the CPA firm's approach. For example, pick samples from the period, not the best examples.
- Access reviews and leaver removals
- Change approvals in the code repository
- Vendor reviews
- Incident records
- Backup restore tests
Turning the review into evidence
Record what you sampled, what you found and how you fixed it. Also keep dates, because a Type II report covers a period. As a result, the review becomes part of your monitoring evidence.
In addition, share results with leadership. The criteria expect oversight, so a short summary helps.
How Ridgeline helps
We run readiness reviews that mirror CPA firm sampling, then help fix what we find. Readiness sits inside our fixed fee of $5,000 to $40,000. We are not a CPA firm, so we prepare and a licensed firm examines. The criteria are in the AICPA Trust Services Criteria.
SOC 2 internal audit questions
Is a SOC 2 internal audit required?
Not as a separate report. However, monitoring is part of the criteria, and a review supports it.
When should a SOC 2 internal audit happen?
Before fieldwork, early enough to fix issues and show the fix operating.
Can a SOC 2 internal audit replace the CPA firm?
No. Only a licensed CPA firm issues a SOC 2 report.
How large should samples be?
Large enough to be representative, chosen across the whole period.
Related guides
Plan your SOC 2 internal audit
Answer four scoping questions. We reply in writing with a scope and a price range, usually the same working day. Also tell us your planned fieldwork date, because timing decides how much fixed evidence can build up. So the review lands when it helps most.
See if we can help