Guide
SOC 2 backup requirements: backups are easy, restores are the test
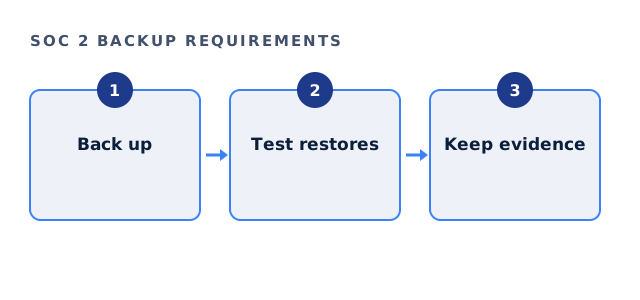
SOC 2 backup requirements are mostly about proving you can recover. So having backups is the start, but evidence of a successful restore test is what usually decides the result.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
Where SOC 2 backup requirements come from
Backups support the Security criteria through business continuity under CC9.1. Also, if Availability is in scope, A1.2 and A1.3 cover recovery and its testing directly. The text is in the AICPA Trust Services Criteria.
What a sound backup setup includes
Cloud services make most of this a setting. Therefore the gaps are usually in testing and documentation.
- Automated backups of production data
- Encryption of backups
- Copies stored separately from production
- Retention stated in policy
- Regular restore tests with records
SOC 2 backup requirements check
Tick what you can prove.
Your result appears here as you tick, so you can see what is still open.
How often SOC 2 backup requirements expect testing
The criteria do not set intervals. However, your policy must, and you must follow it.
| Activity | Common practice |
|---|---|
| Database backups | Daily or continuous. |
| Restore test | At least annually, often quarterly. |
| Policy review | Annually. |
Evidence for SOC 2 backup requirements
Keep backup configuration screenshots and job reports. Also keep a record of each restore test, including what was restored and how long it took, because auditors ask for it.
Part of readiness
We document backups and design the restore test with your engineers, inside the fixed readiness fee. A licensed CPA firm examines the result later.
Make the restore test realistic, and run it the way a real recovery would happen. For example, restore a recent database snapshot into a separate environment and check that the application can read it. Also time the exercise, because recovery time is what a customer actually cares about. Then write down what went wrong, if anything, and fix it before the next test. That record is often the single most persuasive piece of evidence, so keep every one, even the tests that went badly.
SOC 2 backup requirements questions
Are SOC 2 backup requirements stricter with Availability in scope?
Yes. A1.2 and A1.3 make recovery and testing explicit.
Is a cloud provider's backup enough?
Often, but you must confirm it is configured and tested.
How should we document SOC 2 backup requirements?
In a backup policy, plus job reports and restore test records.
What is the most common gap?
No evidence of a restore test.
Related guides
Prove you can recover before the auditor asks
Tell us your stack. We reply with a written scope and a fixed fee.
See if we can help