Service
SOC 2 vendor management that keeps evidence each year
SOC 2 vendor management shows that you know which third parties touch your data and that you check them. So the examination looks for a list, a risk tier and a review record for each important vendor.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
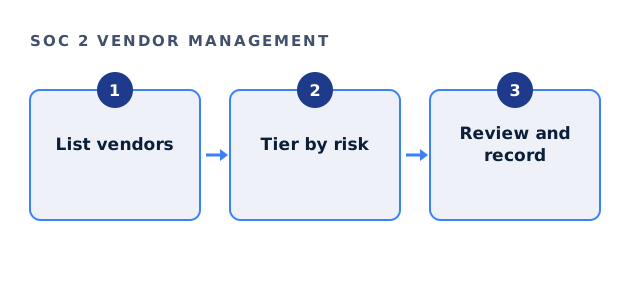
What auditors expect from SOC 2 vendor management
Criterion CC9.2 covers risks from vendors and business partners. Therefore auditors look for a current vendor list, a way of rating risk and evidence that key vendors were reviewed. The criterion text is in the AICPA Trust Services Criteria.
Building the vendor list
Start with anything that stores, processes or can reach customer data. Also include tools with admin access to your systems.
- Cloud hosting and databases
- Email, support and CRM tools holding customer data
- Payment processors
- Contractors with system access
SOC 2 vendor management check
Tick what you have today.
Your result appears here as you tick, so you can see what is still open.
Tiering vendors for SOC 2 vendor management
Not every vendor needs the same review. So tier them, then review proportionately.
| Tier | Example | Review |
|---|---|---|
| High | Hosting provider. | Read their SOC 2 report annually. |
| Medium | Support desk with customer data. | Security questionnaire or report. |
| Low | Design tool with no data. | Listed, but no formal review. |
Reading reports in SOC 2 vendor management
When a vendor shares its report, check the period, the opinion and any exceptions. Also read the complementary user entity controls, because those are duties the vendor expects you to perform. Missing them is a common finding.
SOC 2 vendor management as part of readiness
We build the list, the tiers and the review records with you, as part of our fixed readiness fee. However, the CPA firm examines the result, since we are not a CPA firm.
Keep the process light enough to repeat. For example, a short intake form for new tools, plus an annual review of the high tier, is usually enough for a small company. Also record any decision to accept a risky vendor, because a documented decision is evidence too. That way the examination finds a process, not a scramble.
SOC 2 vendor management questions
Do all vendors need a SOC 2 report?
No. High-risk vendors usually should have one, while low-risk ones can be listed only.
What if a vendor has no report?
Use a questionnaire or other evidence, and record the decision.
How often is SOC 2 vendor management reviewed?
Annually for key vendors, and before onboarding new ones.
What are complementary user entity controls?
Duties a vendor expects you to perform, so you must show you do them.
Related guides
Set up SOC 2 vendor management
Send a rough vendor list. We reply with a written scope and a fixed fee.
See if we can help