Guide
A SOC 2 controls list in plain words
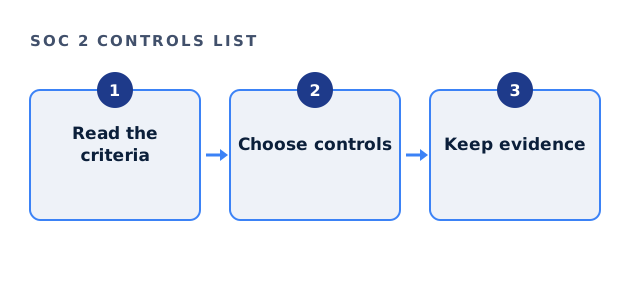
There is no official SOC 2 controls list. Instead, the AICPA publishes criteria, and each company designs controls to meet them. So the list below shows the controls most companies end up with, grouped by criteria.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
Why there is no fixed SOC 2 controls list
The AICPA Trust Services Criteria describe outcomes, not tools. Therefore a startup and a bank can meet the same criterion in very different ways. Your controls must fit your size, but also prove the outcome.
A typical SOC 2 controls list by Common Criteria
Security-only scopes are built on the Common Criteria, numbered CC1 to CC9.
| Criteria | Typical controls |
|---|---|
| CC1 to CC2 governance | Code of conduct, org chart, security roles. |
| CC3 risk assessment | Annual risk assessment, so threats are recorded. |
| CC5 control activities | Approved policies and procedures. |
| CC6 access | Unique accounts, MFA, access reviews, offboarding. |
| CC7 operations | Logging, monitoring and incident response. |
| CC8 change | Reviewed and approved changes. |
| CC9 risk mitigation | Vendor reviews and business continuity. |
Check your SOC 2 controls list
Tick the controls you run and can prove.
Your result appears here as you tick, so you can see what is still open.
Evidence for each control
Every control needs proof that it ran. For example, an access review needs a dated record, while change management needs approved pull requests. So design controls that leave evidence naturally.
Extra controls for extra criteria
Availability adds backup, recovery and capacity controls. Confidentiality adds classification and disposal. However, only add them if a customer asked, because each adds cost.
Turning a SOC 2 controls list into readiness
A list is a start, but the work is matching it to your stack and closing gaps. That is what our readiness engagement does, at a fixed fee of $5,000 to $40,000. We are not a CPA firm, so the examination is separate.
Also remember that controls overlap. For example, a single onboarding checklist can support access, training and asset controls at once, so one good process often satisfies several criteria. That keeps the list shorter and the evidence easier to collect.
SOC 2 controls list questions
How many controls are on a typical SOC 2 controls list?
Often 60 to 120, depending on scope and how controls are grouped.
Is there an official AICPA controls list?
No. The AICPA publishes criteria, so each company designs its own controls.
Can we download a SOC 2 controls list?
Templates exist. However, adapt them, because the auditor tests what you claim.
Do tools generate the controls?
Platforms suggest controls and gather evidence, but you still design and run them.
Related guides
Turn the SOC 2 controls list into your controls
Tell us your stack and criteria. We reply with a written scope and a fixed fee.
See if we can help