Service
SOC 2 policies that match how your team really works
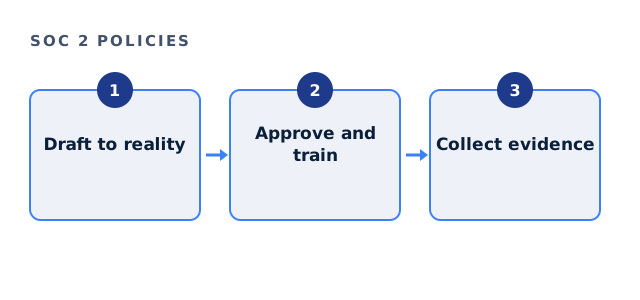
SOC 2 policies tell the auditor what you promise to do. However, the examination then checks whether you did it, so a policy copied from a template becomes a liability if nobody follows it.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
Which SOC 2 policies auditors usually expect
The exact set depends on scope. Still, most Security-only scopes need a familiar core set.
- Information security policy
- Access control policy
- Change management policy
- Incident response plan
- Vendor management policy
- Risk assessment policy
- Business continuity and backup policy
Why template SOC 2 policies fail
Templates promise controls you may not run. For example, a template might require quarterly access reviews, while your team has never done one. Therefore the auditor finds an exception, even though a lighter policy would have passed.
SOC 2 policies quick check
Tick what you have. Gaps here are among the easiest to close.
Your result appears here as you tick, so you can see what is still open.
Writing to the real stack
We write each policy around the tools and team you have. So a 15-person company gets policies a 15-person company can follow, while a larger team gets more structure.
| Policy promise | Evidence the auditor asks for |
|---|---|
| Access reviewed quarterly | Signed review records, so four per year. |
| Changes reviewed before deploy | Pull requests with approvals. |
| Staff trained annually | Training completion records. |
Keeping SOC 2 policies alive
Policies need annual review and approval, because auditors check dates. Also, staff should acknowledge them, so there is proof they were read.
Where policies fit in readiness
Policy writing is part of our fixed readiness fee of $5,000 to $40,000. We are not a CPA firm, so we prepare; a licensed CPA firm examines. The criteria the policies serve are in the AICPA Trust Services Criteria.
A short example shows the difference. A 12-person team promising monthly vendor reviews will miss some, so the auditor records an exception. However, the same team promising an annual review of key vendors can meet it every time. Both policies are acceptable, but only one survives the examination. Therefore we write promises your team can keep, and then we help you keep them.
SOC 2 policies questions
How many SOC 2 policies do we need?
Usually around seven to fifteen, depending on scope and team size.
Can we use templates?
As a starting point, yes. But edit them to match reality, because the auditor tests what you promise.
How often should SOC 2 policies be reviewed?
At least annually, with dated approval.
Do policies alone pass SOC 2?
No. The controls must also run, and evidence must show it.
Related guides
Get SOC 2 policies written for your team
Tell us your stack and team size. We reply with a written scope and a fixed fee.
See if we can help