Service
A SOC 2 readiness assessment that tells you what would fail today
A SOC 2 readiness assessment compares how you work now with what the Trust Services Criteria demand. So you learn what would fail the examination before a CPA firm ever looks.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
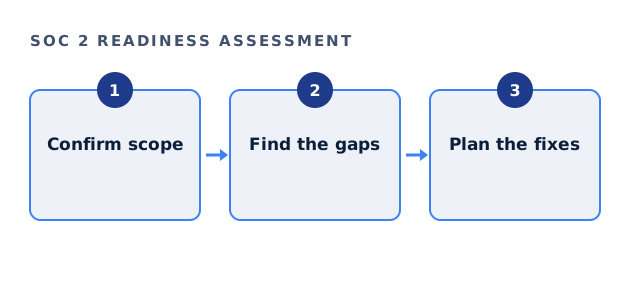
What a SOC 2 readiness assessment covers
We start with the criteria your customer actually asked for, because scope drives everything else. Then we walk through each control area with your team.
- Access control, onboarding and offboarding
- Logging, monitoring and incident response
- Change management and code review
- Vendor management and risk assessment
- Policies and the evidence that they run
What you receive
You receive a ranked list of gaps, so the ones most likely to fail come first. Also, each gap has an owner, a date and a suggested fix. As a result, the readiness work can start the next day.
Quick SOC 2 readiness assessment self-check
Tick what is already true. Each open item is a likely gap, so it will appear in the full assessment.
Your result appears here as you tick, so you can see what is still open.
How long a SOC 2 readiness assessment takes
Gap analysis usually takes two to four weeks. However, the total path depends on the report type.
| Report | Total time | Why |
|---|---|---|
| Type I | 1 to 3 months. | It is a snapshot, so no watch period. |
| Type II | 6 to 12 months. | It includes a watch period of three to six months. |
Readiness is not the audit
We are not a CPA firm, so we do not examine you or issue a report. Instead, a SOC 2 readiness assessment prepares you, and a licensed, independent CPA firm performs the examination later. The criteria themselves are published in the AICPA Trust Services Criteria.
What a SOC 2 readiness assessment costs
It sits inside our fixed consultant fee of $5,000 to $40,000 for the full readiness engagement. Small teams with tidy systems sit near the bottom, while complex stacks with nothing written down sit near the top.
SOC 2 readiness assessment questions
Is a SOC 2 readiness assessment required?
No, but it is the cheapest way to avoid failing. Otherwise gaps surface during the examination, which costs more.
Can the CPA firm do our readiness work?
No. A firm may not examine controls it helped design, so readiness and examination are separate.
Do we need Vanta, Drata or Secureframe first?
No, although they help, because they automate evidence. They do not fix gaps, however.
What happens after the SOC 2 readiness assessment?
Remediation starts, so the evidence trail begins building for the watch period.
Related guides
Book a SOC 2 readiness assessment
Answer four scoping questions. We reply in writing with a scope and a price range, usually the same working day.
See if we can help