Service
A SOC 2 risk assessment that drives your controls
A SOC 2 risk assessment records what could go wrong, how likely it is and what you do about it. So it is not paperwork for its own sake: it is the reason each control exists.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
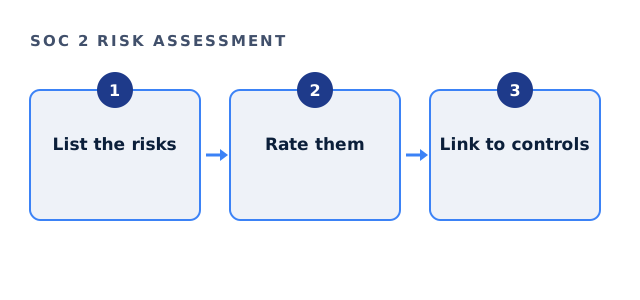
What the criteria expect from a SOC 2 risk assessment
Common Criteria CC3 asks you to identify and analyse risks to your objectives, including fraud and change. Therefore auditors look for a dated, approved assessment that covers those areas. The wording is in the AICPA Trust Services Criteria.
How we run it
We work through your systems, data and vendors with your team. Then each risk is rated and linked to a control.
- Identify assets and data that matter
- List threats and weaknesses for each
- Rate likelihood and impact
- Decide: reduce, accept, transfer or avoid
- Link each decision to a control and an owner
SOC 2 risk assessment check
Tick what is already in place.
Your result appears here as you tick, so you can see what is still open.
A simple rating scale
A clear scale is easier to defend than a complex one. So most small teams use three or five levels.
| Rating | Likelihood | Impact |
|---|---|---|
| High | Expected within a year. | Customer data exposed or service down. |
| Medium | Possible within a year. | Limited data or short disruption. |
| Low | Unlikely. | Minor, internal only. |
How often to repeat a SOC 2 risk assessment
At least annually, and after significant change. For example, a new product or a new major vendor should trigger an update, because the risks have changed.
Where it fits in readiness
A missing risk assessment is one of the most common gaps. However, it is also one of the quickest to close, so we do it early. It is part of our fixed readiness fee, while the CPA firm examines it later.
A useful habit is to review the register whenever something changes. For example, a new payment provider or a new country of operation should prompt a quick update. As a result, the annual review becomes a confirmation rather than a rewrite, and the auditor sees a living document instead of a one-off exercise.
SOC 2 risk assessment questions
Is a SOC 2 risk assessment mandatory?
Yes, in effect, because CC3 requires risk identification and analysis.
How long is a typical document?
A few pages plus a risk register, so it stays usable.
Who should approve the SOC 2 risk assessment?
Leadership, so the auditor sees management owns the risks.
Can we use a spreadsheet?
Yes. Format matters less than coverage and dates.
Related guides
Get your SOC 2 risk assessment done properly
Tell us your team size and systems. We reply with a written scope and a fixed fee.
See if we can help