A SOC 2 compliance consultant who gets you audit‑ready in weeks
A customer asked for your SOC 2 report, and a deal is now sitting still. A SOC 2 compliance consultant finds what is missing, fixes it with your team, and hands a clean file to the auditor.
Read this first. We are not a CPA firm. We provide SOC 2 readiness, gap analysis, and preparation consulting. The formal SOC 2 examination and report are performed by a separate, licensed, independent CPA firm. We do not perform audits or issue SOC 2 reports.
Four questions, about one minute. No phone number, and no call to book.
SOC 2 compliance consultant cost estimator
LiveBuilt from published US market figures for 2025 and 2026. Adjust the four things that actually move a SOC 2 compliance consultant fee.
An estimate from market ranges, not a quote. Your real number depends on your systems. Send us the same four answers and we reply with a scoped range in writing.
Get this scoped properlyTeams who hired a SOC 2 compliance consultant
Security and engineering teams rely on us to get audit-ready without derailing the roadmap.
Logos are the property of their respective owners.
Why the deal is stuck without a SOC 2 compliance consultant
Almost nobody wakes up wanting SOC 2. Instead a buyer sends a security questionnaire, and suddenly a signed contract depends on a report you do not have.
What happens without a SOC 2 compliance consultant
Someone downloads a checklist and starts writing policies. Three months later the policies exist, but nothing is tracked, so the auditor still says no.
Why delaying a SOC 2 compliance consultant costs money
Type II needs a watch period of three to six months. Because that window cannot be shortened, every week you wait is a week added to the end.
The mistake a SOC 2 compliance consultant prevents
Many teams put all five criteria in scope when the customer only asked for Security. As a result the bill grows by about 40 percent for no reason.
What a SOC 2 compliance consultant actually does
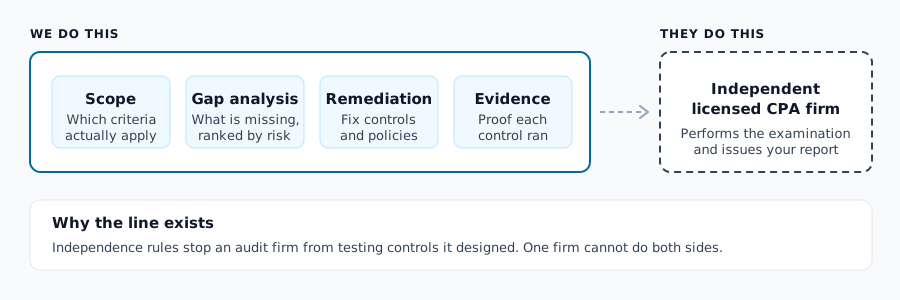
First, a plain answer to the question most first-time buyers ask. A consultant prepares you. An auditor judges you. They cannot be the same firm, because the rules say an audit firm may not test controls it designed itself.
A SOC 2 compliance consultant sets the scope
Your SOC 2 compliance consultant works out which criteria your customer actually requires. Then we write down what is outside the scope, because fuzzy edges are the top cause of overruns.
A SOC 2 compliance consultant finds the gaps
Your SOC 2 compliance consultant compares what you do today against what the criteria demand. You get a list of what is missing, ranked by what would fail the exam first.
Your SOC 2 compliance consultant writes the policies
You get policies that match your real stack and team size. Templates alone do not survive an auditor who asks to see the thing working.
A SOC 2 compliance consultant fixes the controls
Access reviews, logging, onboarding, offboarding, change approvals, vendor lists. A SOC 2 compliance consultant should work alongside your engineers, rather than send a report and leave.
Evidence your SOC 2 compliance consultant collects
Auditors want proof, not promises. So we set up the screenshots, logs, and tickets that show each control ran on the days it was supposed to.
How a SOC 2 compliance consultant hands off
We package everything the licensed CPA firm needs and stay in the room while they test. Afterwards they issue the report, and we never touch that part.
How working with our SOC 2 compliance consultant team runs
A good SOC 2 compliance consultant runs four stages, and you always know which one you are in.
Scope
We confirm the criteria, the systems, and the date your customer expects. Then we fix the fee, so the number does not move later.
Gap analysis
Two to four weeks. You receive a ranked list of gaps and a repair plan with owners and dates against every item.
Remediation
We close the gaps with your team. Meanwhile the evidence trail starts building, which is what the Type II watch period will later measure.
What a SOC 2 compliance consultant does at audit time
The independent CPA firm runs the examination. We answer their questions, chase the missing artefacts, and keep your engineers focused on shipping.
Type I or Type II: how a SOC 2 compliance consultant chooses
Buyers often say they need SOC 2 without knowing there are two reports. Here is the difference in plain words.
| Type I | Type II | |
|---|---|---|
| What it proves | Your controls were designed correctly on one specific day. | Your controls actually ran correctly over a period of months. |
| Watch period | None. It is a snapshot. | Three to six months, and it cannot be skipped. |
| Total time | 1 to 3 months | 6 to 12 months |
| Auditor fee | $5,000 to $30,000 | $10,000 to $70,000 |
| Who accepts it | Some buyers, usually as a stopgap. | Nearly every enterprise buyer, eventually. |
| Best when | You need something credible in hand fast. | You have time, or the buyer already refused a Type I. |
If a deal is blocked right now, then a Type I buys breathing room while the Type II window runs underneath it. Still, ask your customer first, because some of them will not accept a Type I at all.
The five criteria your SOC 2 compliance consultant scopes
SOC 2 is built on five Trust Services Criteria. Only the first is required. Each extra one adds real cost, so this is the single most important thing to get right before you start.
Security
Always required. It covers keeping people out who should not be in: access control, monitoring, and how you handle an incident.
Availability
Your system stays up as promised. Adds roughly 10 to 25 percent. Ask for it only when you sell an uptime commitment.
Confidentiality
Sensitive data stays restricted and gets destroyed on schedule. Also adds about 10 to 25 percent.
Processing Integrity
Your system processes data completely and accurately. Adds 30 to 50 percent, so it is worth confirming the buyer truly asked for it.
Privacy
Personal information is handled the way your notice says. Also adds 30 to 50 percent, and it is the one most often added by mistake.
The SOC 2 compliance consultant rule of thumb
Go back to the customer and ask which criteria they need in writing. Otherwise you may pay for two extra criteria nobody ever wanted.
What a SOC 2 compliance consultant costs, before you talk to anyone
Most firms hide this. We would rather you know now, because a surprise at proposal stage wastes both our time. So here is what a SOC 2 compliance consultant costs in the United States today.
The SOC 2 compliance consultant fee
A fixed SOC 2 compliance consultant fee, set once the scope is agreed. Small teams with tidy systems sit near the bottom. Complex stacks with nothing written down sit near the top.
The CPA firm’s fee
Paid directly to the licensed firm, never to us. Type I sits at the low end. A large Type II sits at the high end.
Typical all-in, first year
The common range for a startup or mid-market software company. Later years cost less, because the hard work is already done.
Your SOC 2 compliance consultant, and who else is involved
Ridgeline Compliance is the SOC 2 readiness practice within Quantum Group. We hold the client relationship and stay accountable for the engagement. Specialist and licensed work is carried out by vetted partner firms under contract to us.
Your SOC 2 compliance consultant is accountable to you
You contract with Ridgeline Compliance. One agreement, one fixed fee, one point of contact.
Licensed examination
An independent licensed CPA firm performs the examination and issues your report. Always separate from us.
Specialist partners
Technical remediation and testing are delivered by partner firms working under contract to us, with insurance in place.
Where your SOC 2 compliance consultant works from
You always contract with Ridgeline Compliance, whichever office your engagement runs from. Work is delivered remotely across US and UK time zones, so evidence review does not wait for a flight.
Boston
Massachusetts, United States
1 Beacon StreetBoston, Massachusetts
United States
London
United Kingdom
169 PiccadillyLondon W1J 9EH
United Kingdom
SOC 2 compliance consultant questions buyers ask first
What is the difference between a SOC 2 compliance consultant and an auditor?
A SOC 2 compliance consultant prepares you for the examination. An auditor, who must be a licensed CPA firm, examines you and issues the report. Confusing the two is the most common mistake first-time buyers make, and hiring one firm to do both is not allowed.
Which report should we get first?
Ask your customer, in writing, before deciding. If they will accept a Type I, take it, because it is faster and cheaper. However, if they insist on a Type II, going through Type I first mostly adds cost rather than saving time.
How long does a SOC 2 compliance consultant take?
Type I usually runs one to three months. Type II usually runs six to twelve months, and most of that is the watch period, which cannot be shortened by spending more. So the earliest useful day to start is today.
Do we need Vanta, Drata, or Secureframe?
No, although they help. Those platforms automate evidence collection, which saves a SOC 2 compliance consultant real time. Still, none of them fixes a missing control or writes a policy that matches your stack, so the readiness work happens either way.
Can a SOC 2 compliance consultant guarantee we pass?
No, and you should walk away from any SOC 2 compliance consultant who does. The opinion belongs to an independent CPA firm. What we can do is make sure nothing predictable is missing before they start looking.
Why is there no phone number on this site?
Because four questions tell a SOC 2 compliance consultant more than a discovery call would, and it respects your time. Answer them and you get a written scope and a price range back, rather than a calendar link.
What does a SOC 2 compliance consultant do after the report?
SOC 2 repeats every year. Afterwards the cost usually drops, because the controls already run and the evidence already collects itself. We can stay on for the yearly cycle or hand everything over to your team.
Ask a SOC 2 compliance consultant for a real number
These four answers are what any SOC 2 compliance consultant needs to price the work. That is not a screening exercise, it is genuinely how SOC 2 readiness is scoped, and it is why we can quote a range without a call.