Service
A SOC 2 gap assessment ranked by what fails first
A SOC 2 gap assessment is a line-by-line comparison of your controls against the criteria in scope. So instead of a vague worry, you get a list of exactly what is missing.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
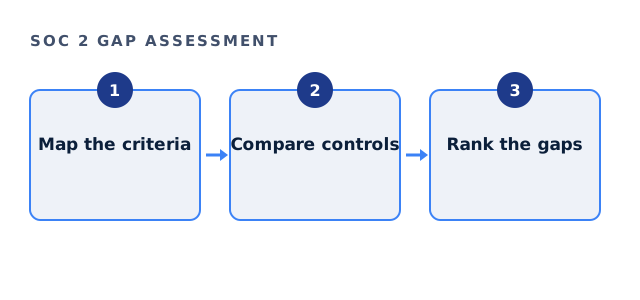
How a SOC 2 gap assessment works
We take each criterion in scope and ask two questions. First, does a control exist? Second, can you prove it ran? A control that exists but leaves no evidence is still a gap, because an auditor needs proof.
Common gaps we find
Most first-time companies share the same handful of gaps. Therefore we check these early.
- No written risk assessment
- Access reviews that never happen
- Offboarding that leaves accounts active
- Changes deployed without review
- No vendor list or vendor review
Mini SOC 2 gap assessment
Tick what you can prove today, not just what you do. Evidence is what counts.
Your result appears here as you tick, so you can see what is still open.
How gaps are ranked in a SOC 2 gap assessment
Not every gap matters equally. So each one is ranked by how likely it is to fail the examination.
| Rank | Meaning |
|---|---|
| Fail | Would fail the examination, so fix first. |
| Weak | Exists but lacks evidence. |
| Minor | Documentation tidy-up. |
Gap assessment versus readiness assessment
People use the terms loosely. However, the gap assessment is the comparison itself, while readiness includes deciding scope and planning fixes. In practice, both are part of our first stage, which takes two to four weeks.
After the SOC 2 gap assessment
We close the gaps with your engineers, rather than sending a report and leaving. Meanwhile, evidence starts collecting, which is what a Type II watch period later measures. The criteria are set out in the AICPA Trust Services Criteria.
One practical tip helps here. Collect evidence while you fix each gap, rather than at the end, because a Type II later measures months of it. So the gap list doubles as an evidence plan.
SOC 2 gap assessment questions
How long does a SOC 2 gap assessment take?
Usually two to four weeks, depending on scope and how much is documented.
Do you need access to our systems?
Read-only access and screenshots are usually enough, so production is not touched.
Will the SOC 2 gap assessment tell us if we pass?
It tells you what is missing. However, only the CPA firm forms the opinion.
What if we have no policies at all?
That is common, so we write policies that match your real stack.
Related guides
Start your SOC 2 gap assessment
Tell us the criteria and team size. We reply with a written scope and a fixed fee.
See if we can help