Guide
Answering a SOC 2 security questionnaire faster
A SOC 2 security questionnaire often arrives with every enterprise deal. Your controls already answer most questions, so the job is to map them once and reuse the answers.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
Why a SOC 2 security questionnaire still arrives
Some buyers accept the report alone. However, many still send a questionnaire, because their own process requires it. So expect both.
Also some questions go beyond SOC 2 scope, such as product roadmap or insurance. Those need separate owners.
Building an answer library
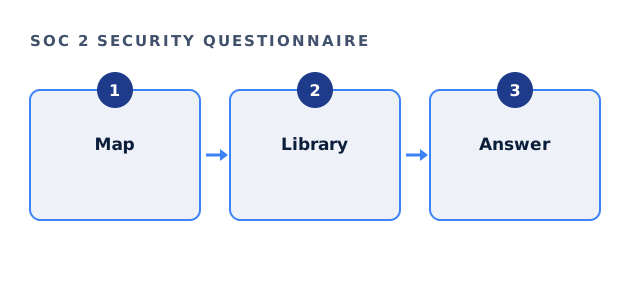
Map common questions to your controls and policies. Then write one approved answer for each. Also note which evidence supports it.
| Question area | Source of the answer |
|---|---|
| Access control | Access policy and review records |
| Encryption | Encryption policy and settings |
| Incident response | Incident plan and exercise record |
| Vendors | Vendor list and review routine |
| Continuity | Continuity plan and test record |
| Report | Current report and bridge letter |
SOC 2 security questionnaire check
Tick what your team already has.
Your result appears here as you tick, so you can see what is still open.
Answering a SOC 2 security questionnaire well
Answer what was asked, briefly. Then point to the report section that covers it. Because reviewers check consistency, answers must match the report.
In addition, avoid promising controls that do not exist. A wrong answer can end up in the contract.
When the report replaces the questionnaire
Some buyers accept the report plus a short addendum. So ask early whether that is possible. It can save days for both sides.
Also offer a written addendum for questions the report does not cover.
Keeping the SOC 2 security questionnaire library current
Review the library when policies change and after each report. Then sales always uses current answers. Also record who approved each answer.
As a result, questionnaires stop pulling engineers away from their work.
Where Ridgeline helps
We build the answer library from your controls and set the review routine. Our readiness fee is fixed, between $5,000 and $40,000. The CPA firm's fee is paid to the firm. The criteria are the AICPA Trust Services Criteria.
SOC 2 security questionnaire questions
Does a SOC 2 report replace a SOC 2 security questionnaire?
Sometimes. Many buyers still send one, so ask early.
Who answers a SOC 2 security questionnaire?
Usually security or compliance, using an approved library.
How long should a SOC 2 security questionnaire take?
With a library, often hours rather than days.
Can answers differ from the report?
They should not. Reviewers compare them.
Related guides
Speed up every SOC 2 security questionnaire
Send us a recent questionnaire. We reply in writing with a library plan and a fixed fee, usually the same working day.
See if we can help