Guide
The SOC 2 control environment, from the top
The SOC 2 control environment is the governance layer under every other control. It covers oversight, structure, conduct and accountability, so leadership produces much of its evidence.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
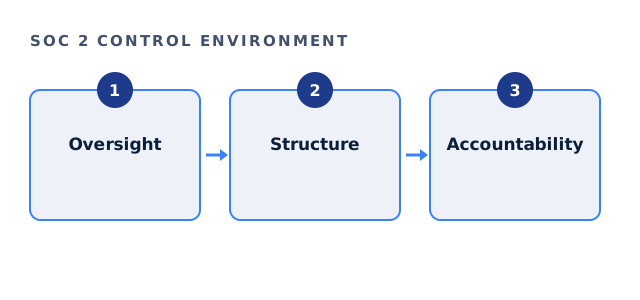
What the SOC 2 control environment includes
The first group of common criteria, CC1, covers the control environment. It looks at integrity and ethics, oversight, structure, competence and accountability.
So it is less about systems and more about how the company is run. Because of that, leaders own most of these controls.
Evidence for the SOC 2 control environment
The firm usually asks for documents and meeting records. The table lists typical items.
| Area | Typical evidence |
|---|---|
| Code of conduct | Policy and employee acknowledgment |
| Oversight | Leadership or board security updates |
| Structure | Organization chart with security roles |
| Competence | Job descriptions and training |
| Accountability | Performance reviews and policy enforcement |
SOC 2 control environment check
Tick what leadership already records.
Your result appears here as you tick, so you can see what is still open.
Oversight records
Leadership should review security regularly, for example each quarter. Then keep minutes or a short summary. Also include risk and incident updates.
In addition, a small company without a board can use a leadership meeting. The firm tests what your policy describes.
Common SOC 2 control environment gaps
The usual gaps are missing meeting records and outdated organization charts. Also code-of-conduct acknowledgments are often missing for older staff.
So run a quick check at the start of the period and fill gaps early.
Linking it to the rest of the program
The control environment sets the tone for every other area. For example, if leadership never reviews risks, the risk assessment looks weak too.
As a result, a strong CC1 file makes the whole report read better.
Where Ridgeline helps
We set up the governance records and brief leadership on what the firm will ask. Our readiness fee is fixed, between $5,000 and $40,000. The CPA firm's fee is paid to the firm. The criteria are the AICPA Trust Services Criteria.
SOC 2 control environment questions
Which criteria cover the SOC 2 control environment?
The CC1 group of the common criteria.
Does a small company need a board for the SOC 2 control environment?
No. Leadership oversight can be shown through regular meetings.
Who owns SOC 2 control environment evidence?
Mostly leadership and the people team.
What is the quickest fix?
Start recording leadership security reviews with dates.
Related guides
Strengthen your SOC 2 control environment
Tell us how leadership reviews security today. We reply in writing with a plan and a fixed fee, usually the same working day.
See if we can help