Guide
Building a SOC 2 project plan that holds
A SOC 2 project plan turns the program into dated milestones with owners. Because several teams share the work, the plan matters as much as any single control.
- Readiness, not the audit
- An independent CPA firm signs
- Written estimate, no call
What a SOC 2 project plan includes
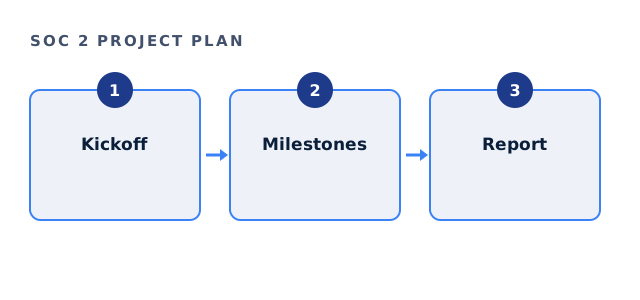
List milestones, owners and dependencies. Also show the decision points, such as the scope sign-off and the start of the observation period.
Then share it with every owner. A plan that only the compliance lead sees tends to slip quietly.
SOC 2 project plan milestones
The table shows a typical sequence. However, your timing depends on how much already exists.
| Milestone | Owner | Typical timing |
|---|---|---|
| Scope signed off | Leadership | Weeks 1 to 2 |
| Gap assessment done | Compliance lead | Weeks 2 to 6 |
| Policies approved | Leadership | Months 2 to 3 |
| Controls operating | Control owners | Months 2 to 4 |
| Observation period | Control owners | 3 to 12 months |
| Fieldwork and report | CPA firm | Several weeks after the period |
SOC 2 project plan check
Tick what your plan already shows.
Your result appears here as you tick, so you can see what is still open.
Dependencies that slow a SOC 2 project plan
Tool changes often take longest. For example, moving to single sign-on or a new ticketing flow. So start them early.
Also watch staff availability. Holidays and launches compete with compliance work, so plan around them.
Reporting progress
Hold a short weekly check with owners. Then send leadership a one-page status every two weeks. Because leaders approve policies and budget, they need to see blockers early.
In addition, keep a risk list for the plan itself, such as a key owner leaving.
Keeping the SOC 2 project plan current
Update the plan when scope changes, not afterward. Also move dates openly rather than compressing later phases. Compressed observation periods help nobody.
As a result, the plan stays a real tool rather than a document.
Where Ridgeline helps
We build the plan, run the weekly check and keep leadership informed. Our readiness fee is fixed, between $5,000 and $40,000. Technical remediation is delivered by partner firms, and the CPA firm's fee is paid to the firm. The criteria are the AICPA Trust Services Criteria.
SOC 2 project plan questions
How long is a typical SOC 2 project plan?
Often six to twelve months to a first Type 2 report, depending on starting point.
Who should own the SOC 2 project plan?
One coordinator, usually the compliance or security lead.
What breaks a SOC 2 project plan most often?
Late tool changes and owners without time set aside.
Should the CPA firm see the plan?
Sharing key dates helps the firm schedule fieldwork.
Related guides
Start your SOC 2 project plan
Tell us your target report date. We reply in writing with a draft plan and a fixed fee, usually the same working day.
See if we can help